European Fridge Hacks Raise Cyber Security Warnings
Cyberattacks that drove temperatures higher in internet-connected refrigerators affected retailers across Europe, while separate incidents targeted a cryptocurrency exchange and Ukraine’s emergency alert app. UK cyber officials warn that artificial intelligence could help attackers exploit weaknesses, but experts say some recent intrusions relied on basic security flaws.
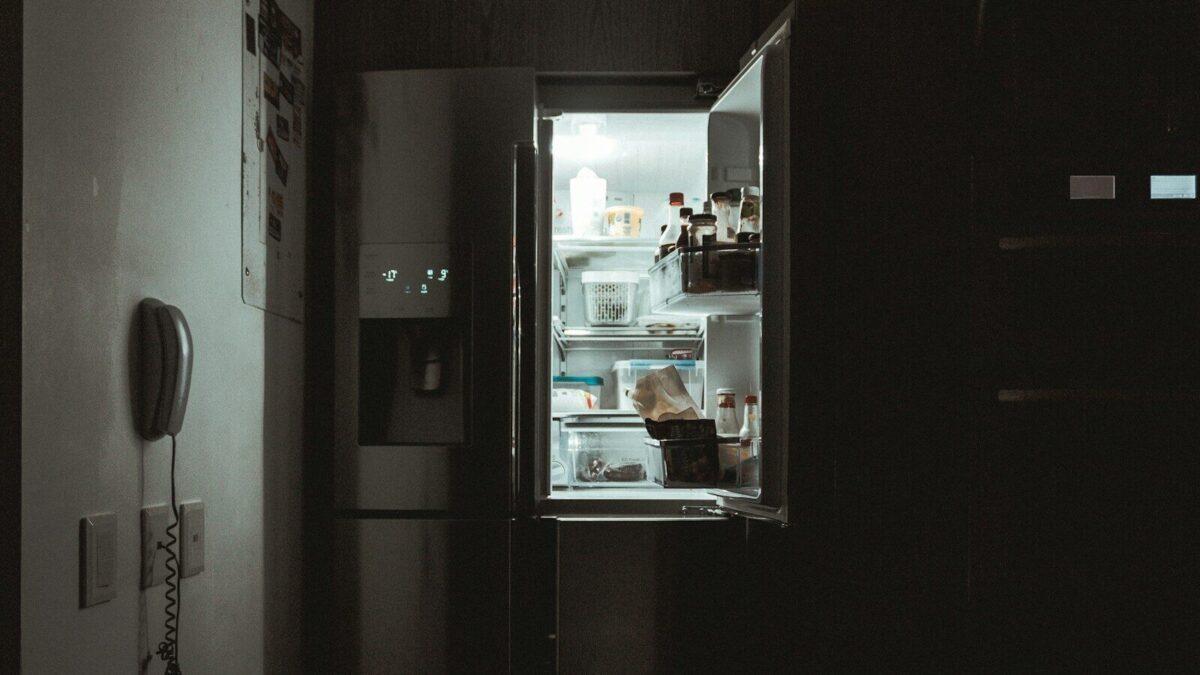
Cyberattacks that overheated internet-connected refrigerators at retailers across Europe have added to warnings that cyber security threats are growing, as artificial intelligence helps expose weaknesses in digital systems. The incidents came alongside a reported $6.3bn heist at cryptocurrency exchange Binance and a fake nuclear alert sent through Ukraine’s emergency app.
The refrigerator attacks affected retailers in Belgium, Estonia, Ireland, Finland, Luxembourg, the Netherlands and Sweden. In some shops, temperatures climbed as high as 50C (122F).
London wholesale business owner Alex Pearce said he spotted defrost lights and a panel reading of 150C on two refrigeration units. He unplugged the internet connection after suspecting an attack.
“If it had happened on a Saturday morning, when I don’t tend to be here, it could ultimately have led to a fire,” Pearce said.
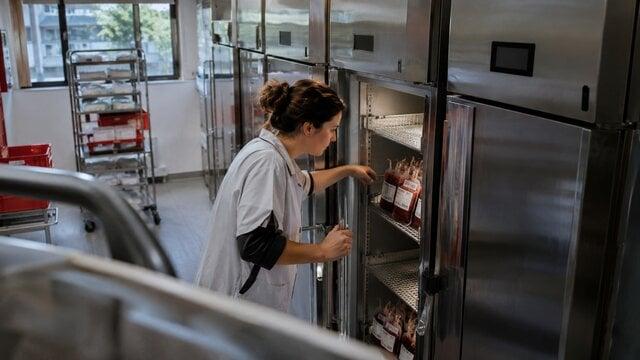
Three sites in France that handle blood and plasma bags were also briefly affected. The Établissement Français du Sang said cold rooms storing blood were “raised to very high temperatures” on November 2, but alarm systems and staff detected the changes before samples were damaged.
On 30 October, hackers stole $6.3bn (£4.7bn) from Binance, the world’s largest cryptocurrency exchange, according to the report. On 1 November, hackers targeted Ukraine’s emergency alert app and sent people in Kyiv a fake warning of a nuclear strike.
Richard Horne, head of the UK’s National Cyber Security Centre (NCSC), said the world was in the “foothills” of a new hacking landscape. Artificial intelligence can expose flaws in information technology systems, he said.
“There are so many vulnerabilities out there that … you could say are waiting to be exploited,” Horne said. He warned that the near-term danger included “a huge rise in the volume of incidents.”
The NCSC said AI-powered malicious software was “highly likely” to be used by 2028 in attacks against UK power stations, airports and hospitals. It said AI could help attackers scout targets, find weaknesses in networks and write malicious code.
Yet the refrigerator attacks may not have required advanced tools. NCSC operations director Paul Chichester said hackers “really didn’t need” AI to find the flaws, which included default access passwords published in one manufacturer’s manuals.
The US Cybersecurity and Infrastructure Security Agency said attacks on cold-storage systems could exploit authentication bypasses, code injection and weak configurations. France’s Danfoss said affected systems “were running outdated firmware” and urged customers to keep products updated.
Who carried out the refrigerator attacks, and whether they were connected, remains unclear. Russian hacktivists claimed responsibility for some incidents without providing credible evidence; the Kremlin denied involvement, while researchers also identified potential links to Iran-linked actors.